In this article, you'll learn how to use North's Embedded Checkout for accepting payments in a React application. In part 2 of this series, you'll learn how to expand on your application by adding a React shopping cart to it.
You can follow along with this Node.js GitHub repo for the back-end web service and this React repo for the front-end ecommerce storefront.
Benefits of Using Embedded Checkout (Form Integration)
How do embedded payments work?
- The customer initiates the checkout process.
- The merchant server makes a secure request to the North session service to create a checkout session.
- The session service returns a short-lived session token (valid for 30 minutes) to the merchant server, which forwards it to the front-end application.
- The client application loads North's lightweight script (
checkout.js) and callscheckout.mount()with the session token to render a secure, responsive payment form directly within your layout. - The customer fills out the payment form and submits it. The form is posted directly to North's PCI-compliant servers.
- The client listens for transaction completion via the
onPaymentCompletecallback and navigates to the confirmation page. - Your server queries the secure session status endpoint to authoritatively verify the transaction result (Approved or Declined) before fulfilling the customer's order.
Implementing Embedded Checkout in React
You can find your test credentials (Checkout ID, Profile ID, and Private API Key) directly in your Embedded Checkout dashboard once you save your first checkout configuration in the Checkout Designer.
Setting Up the Project
paymentshub-react and open it in your terminal. This is the folder that will hold the code for the whole project.
In the next steps, you will create the front-end application and the back-end application. You will then upload these applications to GitHub and deploy them.
Creating the Server
You will create your server using the Express framework. The server will have two routes: one to generate an Embedded Checkout session token, and another to fetch the secure session status after payment completion.
Inside the paymentshub-react folder, create a new folder called api. Open the api folder in your terminal, and run the following command to initialize a Node.js project:
Next, open the api/package.json file and replace the scripts key-value pair with the following:
This script is used to start the Node server.
Make sure you also replace the main key-value pair with the following:
Next, run the following command in the terminal to install the required dependencies:
The purpose of each package is explained below.
cors: enables cross-origin resource sharing.dotenv: loads environment variables from a.envfile.express: creates a Node.js server.node-fetch@2: makes HTTPS requests to North's checkout session endpoints.
Next, create a new file named server.js in the api directory. This will act as the entry point into the Node server. Paste the code below inside the server.js file:
The server.js code contains two essential routes.
The /api/create-checkout-session route is used to generate a secure session token by making a POST request to the North checkout sessions URL.
To authorize this request, you pass your private API key in the Authorization header as a bearer token. The required request body parameters are checkoutId, profileId, the total amount to charge, and an array of products that the customer is purchasing. The response contains a short-lived session token (valid for 30 minutes) which is forwarded to the React front-end application to safely render the prebuilt iframe.
Secondly, the /api/session-status route allows your backend to securely query North's status endpoint using the sessionToken. Since client-side responses can theoretically be modified by users, this server-side endpoint acts as your authoritative source of truth. Your backend should always call this endpoint to verify if a payment status is Approved before fulfilling the purchase or updating your database.
Most of the secrets (such as the CHECKOUT_PRIVATE_KEY) are kept on your server and loaded via environment variables to keep them completely isolated from the front-end client code. You can access the full server code in this GitHub repo .
Building the React Storefront and Embedded Checkout Front-End
paymentshub-react folder and run the following command:
Once the React app is created, navigate to the client folder and run the following command to install the required dependencies:
The purpose of each package is as follows:
bootstrap: to style the React app.react-bootstrap: to provide Bootstrap 5 components that are built with React.react-router-dom: to set up routing in the React app.
First, you need to load North's payment library. Open the client/index.html file and add the script tag inside the <head> block:
This script exposes a global checkout object on the window, which we will use to mount our hosted checkout form.
Next, open the src/main.jsx file and replace the existing code with the following:
This sets up the BrowserRouter for the React app.
Next, open src/App.jsx and replace the existing code with the following:
This imports the BootStrap CSS file and various pages. It sets up four routes for the various pages in this app:
Homepage: to display various products.ProductPage: to display the details of a particular product.Payment: to load and display the Embedded Checkout form.PaymentResults: to show the secure payment result.
First, you will create the components that are used in this application.
Inside the src folder, create a folder called components. In the components folder, create a file called NavBar.jsx and paste in the code below:
This will create a simple navigation bar.
Next, create a file called ProductCard.jsx inside the components folder and add the code below:
The above code creates a reusable card component that you will use to display the details of a product on the homepage.
Now you can go ahead and create the pages. Inside the src folder, create a folder called pages. Make sure you create the files below inside the pages folder.
You will start by creating the Homepage.jsx file. Paste the following code inside this file:
The above code fetches various products from the Fake Store API and uses the ProductCard component to render them on the page.
Next, create a file ProductPage.jsx and paste in the code below:
The above code retrieves the product details based on the navigation parameter and renders them. It contains a button that, when clicked, triggers createCheckoutSession(). This function makes a POST request to /api/create-checkout-session on our backend server and passes a products array with the item details. If successful, it stores the returned token (session token) in local storage and redirects the user to our /payment route where the checkout form will be loaded.
Remember to replace with your actual backend server link once you deploy your API.
Next, create a file called Payment.jsx and paste in the code below:
This page retrieves the sessionToken from local storage and mounts the secure hosted payment form. By calling window.checkout.mount(), North automatically renders a fully optimized, responsive checkout iframe inside the #checkout-container element.
Additionally, we call window.checkout.onPaymentComplete() to register a callback. Once the customer completes their transaction successfully within the secure iframe, this callback runs and navigates them automatically to /payment/result.
This simplifies your client-side code immensely, removing any requirement to build and maintain sensitive input forms for card numbers, expiration dates, or CVV inputs.
Lastly, create a file called PaymentResults.jsx and paste in the code below:
This page makes a GET request to your backend's secure /api/session-status endpoint, passing along the sessionToken. Your backend acts as the secure proxy, requesting the checkout status from North's secure servers, and returns the result. If the status is 'Approved', we display a payment success page showing the transaction ID, auth code, and amount request details. Otherwise, we inform the customer that their payment failed. The exact field names (and whether they appear at the top level or nested under a body object) come from North's Session Status response, so confirm them against a real response from your account and adjust the mapping if needed.
You can access the full code for the React app on this GitHub repo .
Deploying the Front-End and the Back-End Applications
Before deploying, create the file named _redirects in the client/public folder and paste in the content below:
This will instruct Netlify to redirect all the routes to the index.html file. Without this, you won't be able to redirect to a specific page or reload a page.
Next, upload both applications' code to GitHub . Make sure each application has its own, separate repository.
Next, you will deploy your Node Express app on Render . Be sure to set 'npm start' as the Start Command, and that you [configure the following environment variables {"type": "button-naked", "useNewTab": "true", "icon": "external"}]:
CHECKOUT_PRIVATE_KEY: Your Private Embedded Checkout API Key, copyable from your checkout instance page on the dashboard.CHECKOUT_ID: Your unique checkout configuration ID found on your dashboard.PROFILE_ID: Your merchant profile identifier from your merchant list on the dashboard.
To deploy the React app, check out the official Netlify documentation . Because the client-side code doesn't directly handle payment transactions, you do not need to configure any sensitive environment variables on Netlify! This completely eliminates client-side credentials exposure.
Once the deployment completes successfully, copy the deployed Node Express API link. You will use it to replace the placeholder API link in the React app.
Open the client/src/pages/ProductPage.jsx file and replace with the link for your deployed Node Express API. Do the same for the client/src/pages/PaymentResults.jsx file. Once you make these updates, push your changes to GitHub to trigger Netlify to automatically redeploy your React app.
Demonstrating the Final App
Click on View Details for the first product, which will display a page with product details.
Click on Purchase Now. This action requests a session token from your backend server and redirects you to the payment page.
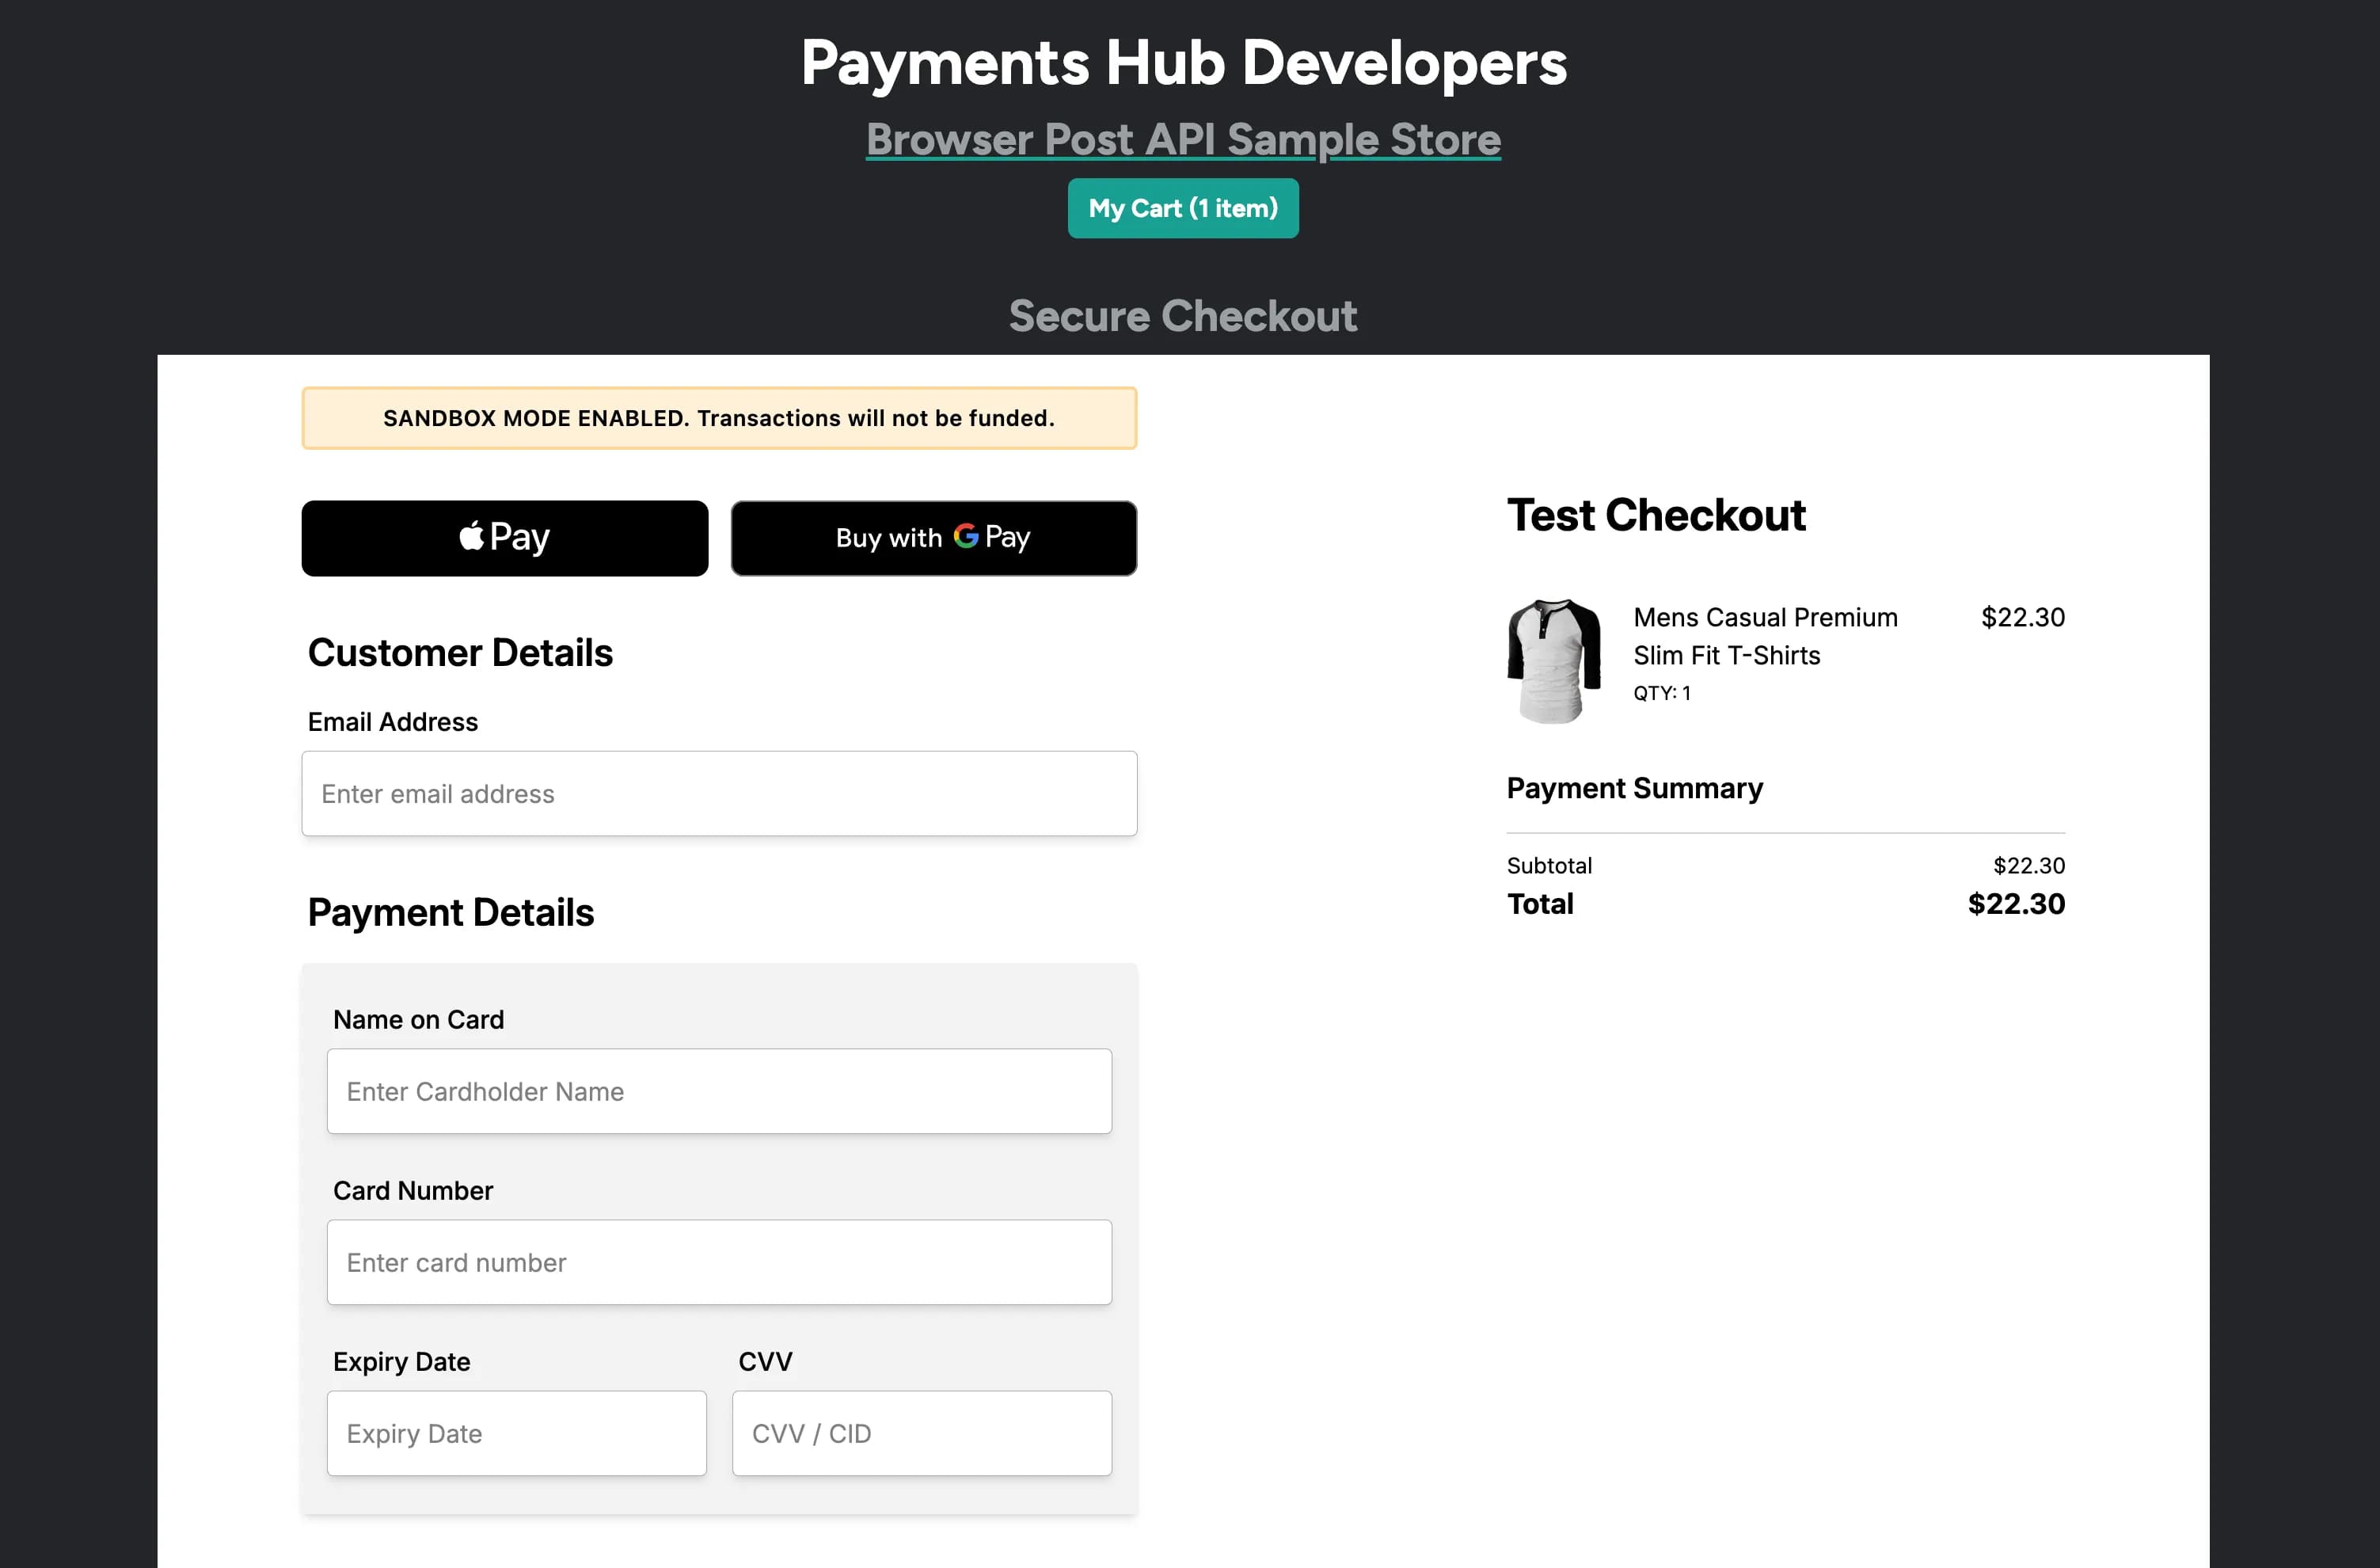
The payment page will mount the secure, prebuilt North Embedded Checkout form, which will display the payment options (including card checkout and digital wallets if configured). Simply enter test card credentials to complete the purchase. The form will securely submit payment info directly to North and trigger our on-payment-complete callback, redirecting you to our success screen.
If you provided incorrect card details (e.g. invalid expiry or card number), the checkout form will show the error details inline or handle the declined status, keeping your customer informed during checkout.
Conclusion: Launching Your Secure React Embedded Checkout
In this guide, you've learned about embedded payments and their benefits. You also learned about North's modern Embedded Checkout (Form Integration) and how to securely integrate it into your React application to build a seamless, secure storefront with minimal compliance requirements. You can read the Embedded Checkout Integration Guides to learn more about how this product can meet your business needs.
To learn how to modify your app to add shopping cart functionality in ReactJS, check out Part 2 of this series.
How To Get Started
Contact North's Sales Engineering team to learn more about how the Embedded Checkout and other tools can meet your business needs.